Granular security that grows with your business
Security isn't just about keeping unauthorized users out—it's about ensuring the right people have access to exactly the right information at the right time. Butterfly's Object Structure Secure Authorization delivers enterprise-grade security with field-level precision control.
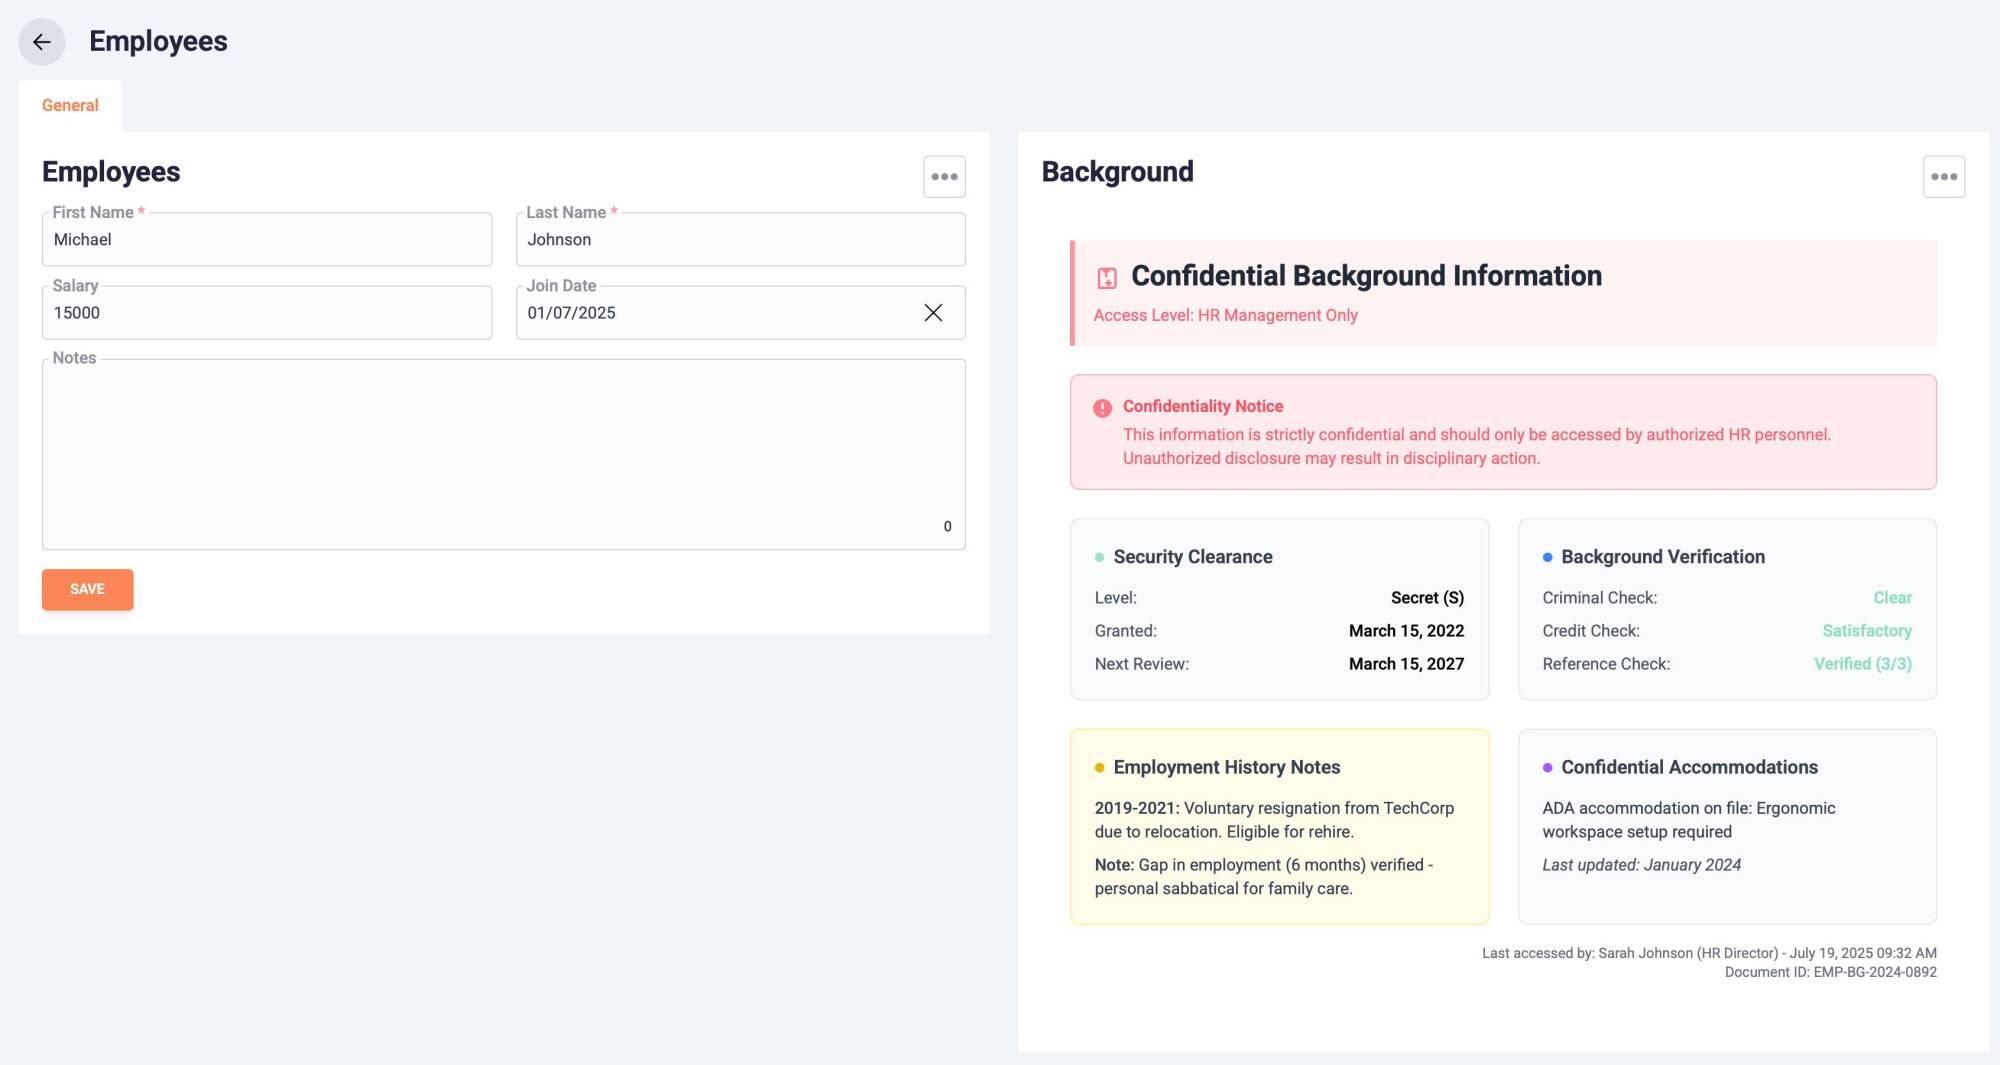
Comprehensive security controls
Field-Level Security
Control access to individual data fields within your objects, going far beyond traditional role-based access control. Marketing teams see product descriptions and images, while finance teams access pricing—neither sees supplier cost information. Precise control without blanket permissions.
Row-Level Permissions
Filter which records users can see based on dynamic conditions. Sales reps only see customers in their territory, managers see all records in their department, and executives have organization-wide visibility. Complete data isolation without complex queries.
Object-Level Permissions
Control who can access specific objects (data structures) in your system. Define View, Edit, Create, Delete, and Approve permissions at the object level. Secure your entire data model with fine-grained authorization that cascades logically through your application.
Role-Based Access Control
Assign permissions to roles rather than individuals. Simplify management with hierarchical role structures and inherit permissions across your organization.
Audit Trail & LDAP Integration
Track who accessed what data and when with tamper-proof audit logs. Seamlessly integrate with Active Directory and LDAP for single sign-on, automatic user provisioning, and inherited organizational structure. Meet GDPR, ISO 9001, and ISO 27001 requirements out of the box.
Workspace-Level Isolation
Segment entire applications using Workspaces, where each acts as a secure boundary. Logistics teams see only logistics objects, marketing teams access only marketing content, finance works in separate workspaces. Perfect for multi-brand enterprises and multi-tenant SaaS applications.
Why Butterfly's security model?
Traditional Security
Most platforms offer basic authentication with limited authorization controls.
- Application-level security only
- Manual permission management
- Limited granularity
- Complex to maintain at scale
- Risk of data leaks
Butterfly Deep Security
Multi-layered security architecture with field, row, and object-level controls built into the platform core.
- Security enforced at data layer
- Automated role-based permissions
- Field and row-level granularity
- Scales effortlessly with growth
- Zero-trust architecture
Frequently Asked Questions
Transform your data security
Butterfly's Object Structure Secure Authorization provides the foundation for truly secure, flexible, and scalable enterprise applications. Protect sensitive data without compromising usability.